The gore and tragedyslop merchants of ArchiveGenocide are back. This time they are not posting heavily edited videos from the Gaza War. They are posting a Python script.
ArchiveGenocide claims to have built a tool to detect “12,100 traces of Israeli spyware” on your devices. They are asking you to download it, run it, and send them your findings via Telegram.
We examined the repository. We analyzed the script. And here is the terrifying truth: The tool is the trap.
The Myth: “Omnipresent Israeli Spy”
First, we have to debunk the paranoia that ArchiveGenocide is exploiting. The internet is flooded with claims that the IDF, Mossad, or Shin Bet are secretly infecting the phones of every pro-Palestinian protester, every Twitch streamer, every YouTuber, every 4chan edgelord, every student radical, every statesperson, every politician, every influencer, every celebrity, every magnate, every businessperson; literally everybody. The math doesn’t math. The idea that the State of Israel is burning zero-day exploits and spending millions to track every random college student in France who is protesting school cafeterias is absurd. It is a techno-blood libel. It relies on the ancient antisemitic trope of the all-knowing, all-powerful Jew who secretly controls the world, but updated for the iPhone era.
The spyware ArchiveGenocide references; Pegasus, Predator, and Graphite, are manufactured by private companies like NSO Group and Cytrox and sold to governments for millions of dollars. These are strategic weapons designed to track cartel bosses, terror cells, and high-value political targets. Afterall, spyware is in fact a global industry. The US has its own cyber-arsenal, including tech giants that are currently facing legal action for spyware, while Russia and China are vastly more pervasive in their aggressive surveillance of Western citizens. Yet oddly enough, Israel, the liberal oasis in an ocean of barbaric authoritarian theocracies, is the surveillance supervillain.
The Trap: Zero Breach Toolkit
Into this manufactured panic about Israel’s omnipresent surveillance capabilities, steps ArchiveGenocide with their “final solution”, boldly claiming the Zero Breach Toolkit “never writes to disk, never connects to the internet, or ask for admin perms.”
But this is a lie, and this is why:
1. Full Disk Access Trojan
The README claims it doesn’t need admin rights. But on macOS, it instructs the user to give Terminal Full Disk Access. This is a massive security risk. Full Disk Access grants the script unrestricted permission to read every single file on your computer. Your iCloud backups, your passwords, your photos, your browser history, your encrypted messaging apps. It is not “admin rights”, but it is a backdoor. A script that asks you to bypass your OS’s core security architecture is not a security tool. It is a breach.
2. Telegram Exfiltration
Once you run ArchiveGenocide’s script and it has scanned your files, the prompt tells you: “If you find some spyware on your device, consider sending it to us via telegram.”
This is the most dangerous part of the operation. Telegram is not end-to-end encrypted by default. It is a known haven for malware distribution and state-sponsored hacking. ArchiveGenocide, a shady, shadowy, anonymous group with a documented history of manipulating data, is asking you to send your sensitive device files to an unsecure channel where they can be harvested, stored, and exploited!
3. Signature-Based Uselessness
Even if ArchiveGenocide’s tool isn’t malicious, it is functionally useless. It uses “signature-based detection” and looks for known file names and indicators. Modern spyware is polymorphic. It is designed to evade exactly this kind of scan. ArchiveGenocide admits this in their own README: “A clean result… does not mean the device is clean.”
ArchiveGenocide know their tool is inadequate. They say so. Then they tell you to run it anyway. So what is the point? The point is data harvesting. The point is creating a false sense of security while you voluntarily hand over your digital footprint, as their tool generates GitHub stars, generates credibility, and creates a database. As thousands of Gen Z and millenial activists continue to run this script and send their “findings” via Telegram, ArchiveGenocide now has a massive map of the devices, vulnerabilities, and personal data of the exact demographics they are trying to mobilize.
ArchiveGenocide: Mask, Voice, Theater
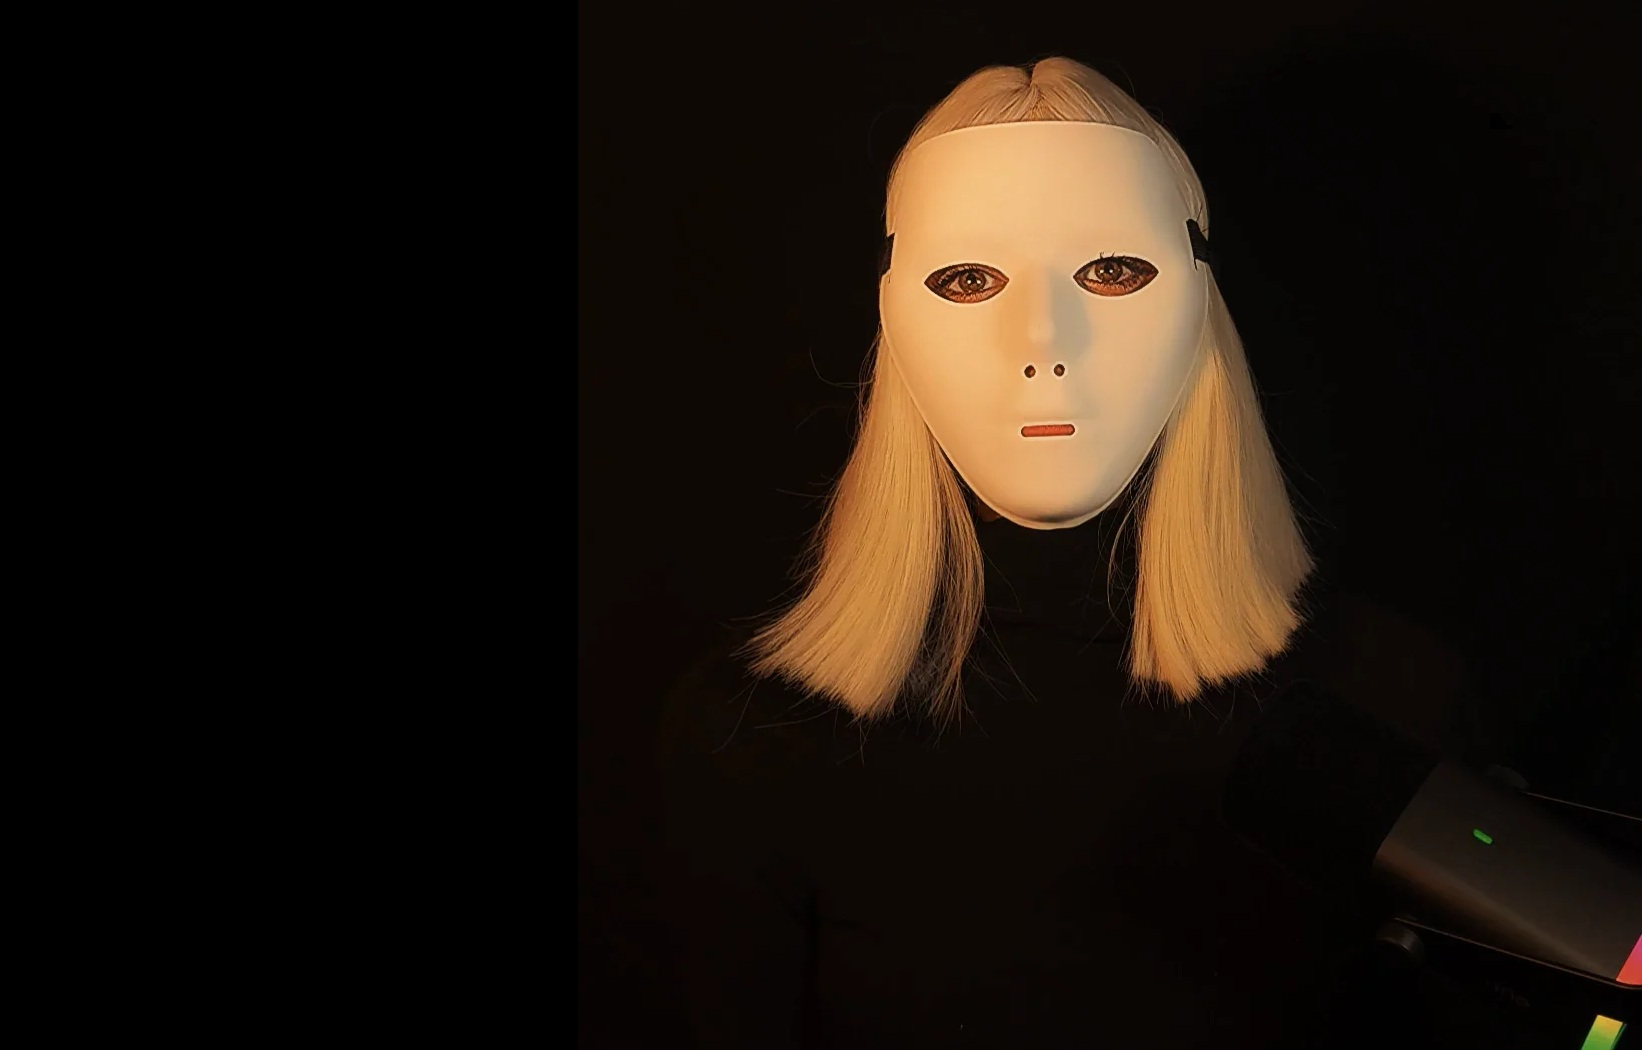
ArchiveGenocide announced the release of this tool using what has now become their signature look: an anonymous representative in a tacky blonde wig, a white Guy Fawkes type mask and a highly distorted voice.
This is not how real security researchers operate. If you go to the Citizen Lab or Amnesty International’s Security Lab, you will find real people with real faces and real credentials. They publish peer-reviewed reports. They don’t hide behind masks because their credibility depends on transparency.
Voice Distortion Breakdown:
The audio uses a standard pitch-shifting effect. You can hear the slight metallic timbre and the flattened formants. It is a basic audio filter, not advanced anonymity tech. It is designed to create an aura of mystery and danger, basically a midwit attempt at turning a data-harvesting operation into a cyberpunk movie – while serving a darker purpose: preventing voiceprinting and accountability – when ArchiveGenocide (or their “IsraelExposed” social media handles) makes false claims about spyware and suddenly there is no identity to trace, no one to subpoena, and no one to hold responsible when users’ devices are suddenly compromised.
The wig, the mask and the voice distortion are not there to protect whistleblowers. They are there to protect botnet builders.
WHAT NOT TO DO
Don’t fall for the techno-blood libel. Israel is not spending millions of dollars to hack your phone because you attended a protest. The narrative is designed to make the gullible feel hunted, radicalized, and important.
Don’t download ArchiveGenocide’s toolkit. A Python script that requires Full Disk Access and directs you to send files via Telegram is downstream from a textbook social engineering attack.
ArchiveGenocide is the threat. They are not trying to protect you. They are trying to compromise you. They are building an arsenal of compromised devices under the guise of “activism”.
WHAT TO DO
If you are actually worried about digital security, don’t let ArchiveGenocide turn your paranoia into their payload. Do this instead:
- Use official security resources, and never download unverified tools from shady groups
- Turn on Two-Factor Authentication (2FA)
- Update your OS, or better yet, go full Linux